
CVE-2026-19412
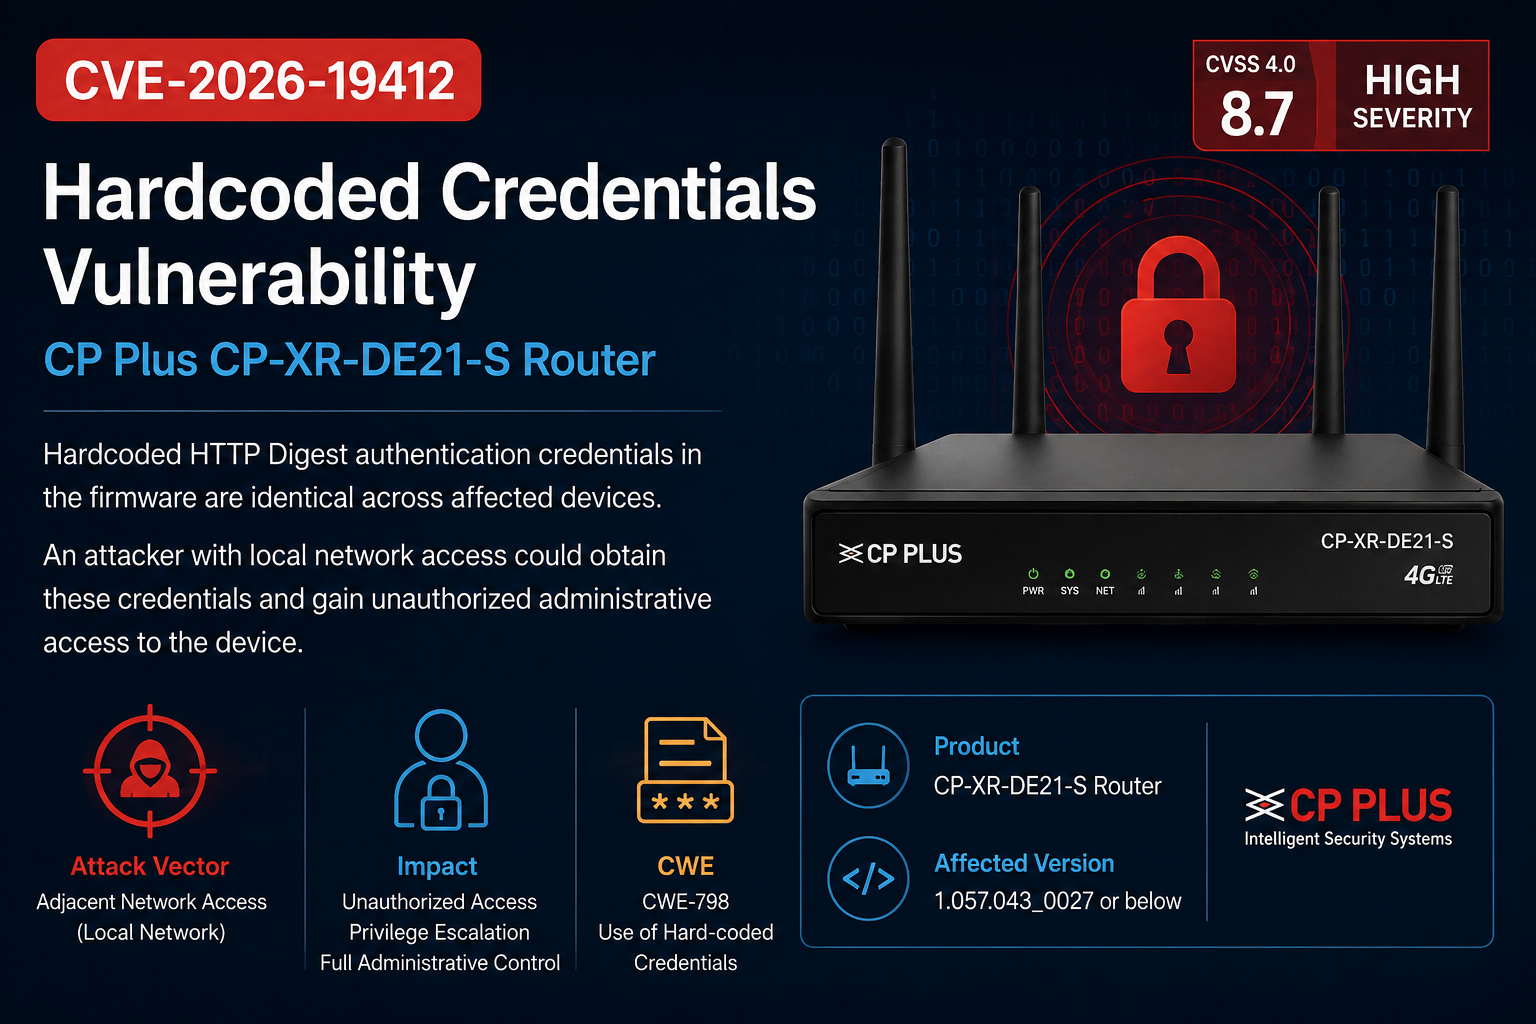
High-severity hardcoded credentials vulnerability in the CP Plus CP-XR-DE21-S Router allows an attacker with local network access to obtain shared HTTP Digest authentication credentials and gain unauthorized administrative access.
Overview
CVE-2026-19412 is a high-severity hardcoded credentials vulnerability affecting the CP Plus CP-XR-DE21-S Router.
The vulnerability exists because the affected firmware contains hardcoded HTTP Digest authentication credentials that are identical across all devices running the vulnerable firmware versions.
An attacker with access to the local network could obtain the hardcoded authentication information from the firmware and use it to authenticate to the affected device.
Technical Description
The CP Plus CP-XR-DE21-S Router uses HTTP Digest authentication for administrative access.
In affected firmware versions, authentication credentials are embedded within the firmware and remain identical across affected devices. This introduces a shared-secret authentication weakness: once the hardcoded credentials are obtained, they can potentially be reused against other devices running the same vulnerable firmware.
The vulnerability is classified as:
- CWE-798: Use of Hard-coded Credentials
- CVSS 4.0: 8.7 (High)
The CVSS vector is:
CVSS:4.0/AV:A/AC:L/AT:N/PR:N/UI:N/VC:H/VI:H/VA:H/SC:N/SI:N/SA:N
The attack vector is Adjacent (AV:A), meaning the attacker must have access to the local/adjacent network environment.
Potential Impact
Successful exploitation could allow an attacker to:
- Obtain the hardcoded authentication information
- Bypass intended device-specific authentication controls
- Gain unauthorized administrative access
- Perform privileged operations on the affected router
- Compromise the router’s confidentiality, integrity, and availability
Because the same credentials are present across affected devices, the risk extends beyond a single router and may affect multiple devices deployed with the vulnerable firmware.
Affected Versions
| Vendor | CP Plus |
| Product | CP-XR-DE21-S Router |
| Affected | 1.057.043_0027 or below |
Remediation
Users and administrators should update affected CP Plus CP-XR-DE21-S Routers to a firmware version that addresses the vulnerability.
Additional defensive measures include:
- Restricting administrative access to trusted local networks
- Preventing untrusted users from reaching the router’s management interface
- Updating firmware on all affected deployments
- Reviewing administrative access and authentication activity after remediation
- Replacing or resetting credentials where supported by the device
Organizations deploying multiple affected devices should prioritize firmware updates across the entire fleet because the vulnerable authentication information is shared across devices running the affected firmware.
Disclosure
The vulnerability was assigned CVE-2026-19412 by the Indian Computer Emergency Response Team (CERT-In), which is the CVE Numbering Authority (CNA) for this record.
The CVE record was published and updated on August 28, 2026.
References
- CVE Record: https://www.cve.org/CVERecord?id=CVE-2026-19412
- CERT-In Advisory: https://www.cert-in.org.in/s2cMainServlet?pageid=PUBVLNOTES01&VLCODE=CIVN-2026-0428
Finder: Stalin S, Harini M, Rohit Surya A T & Reginald Alfret V
CNA: Indian Computer Emergency Response Team (CERT-In)
Research. Remediate. Reinforce.